Security Research for the Community

Recently Added

Research
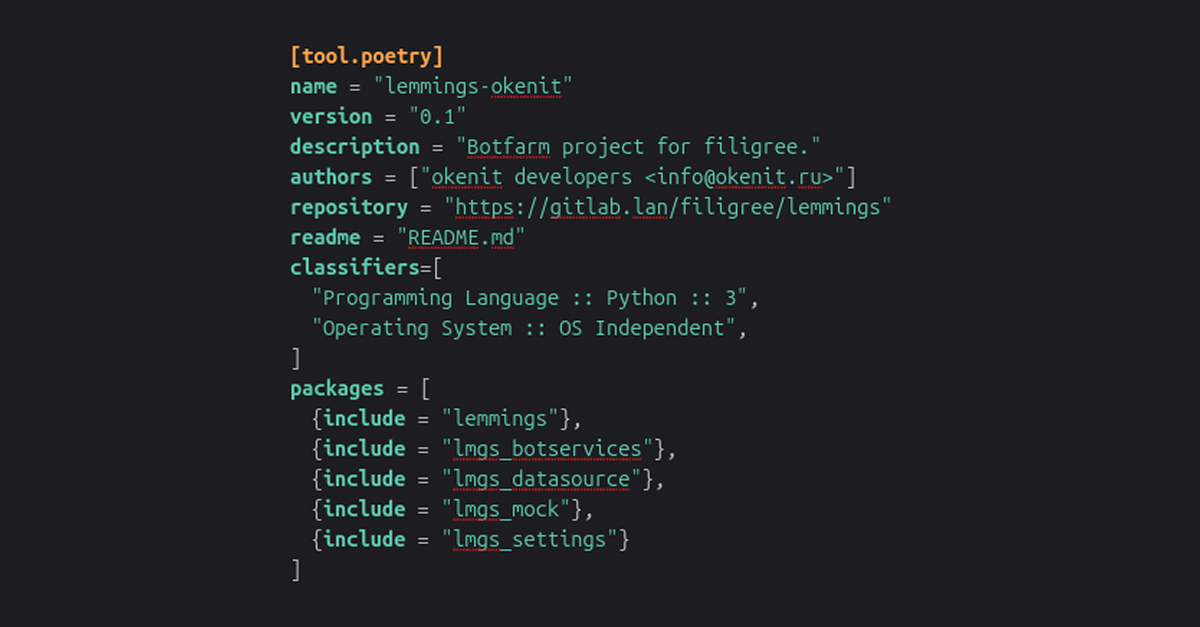
Lemmings: Russian Industrialized Persona Provisioning and Management for Active Measures Campaigns

Leaked internal data from Russian contractor Okenit reveals "Lemmings" (Лемминги)—a Python-based framework designed to industrialize the creation, verification, and management of synthetic online personas for Russian active measures. Built to automate phone verification, email infrastructure, CAPTCHA solving, and anti-detection measures, Lemmings functions as the identity-provisioning layer within a larger ecosystem alongside proxy and tasking tools (SOI and SOS). Live tests against platforms like VK and Reddit demonstrate a shift toward scalable, modular software frameworks capable of maintaining durable cover identities for intelligence, influence, and disinformation operations.

2026-09-16
Research
Threat Intelligence Report: University Leak Exposes Russia’s Military Cyber Training Pipeline

A leaked cache of institutional files reveals that Department No. 4 at Bauman Moscow State Technical University operates as a structured force-generation pipeline for Russian military cyber operations, training roughly 250 students across specializations. Supervised directly by senior GRU leadership, the program blends offensive intrusion, malware analysis, financial-systems targeting, and cryptographic defense with field placements that feed graduates straight into GRU- linked cyber formations like APT28 (Unit 26165) and Sandworm (Unit 74455).

2026-08-26
Research
Chinese Malware Delivery Domains Part V

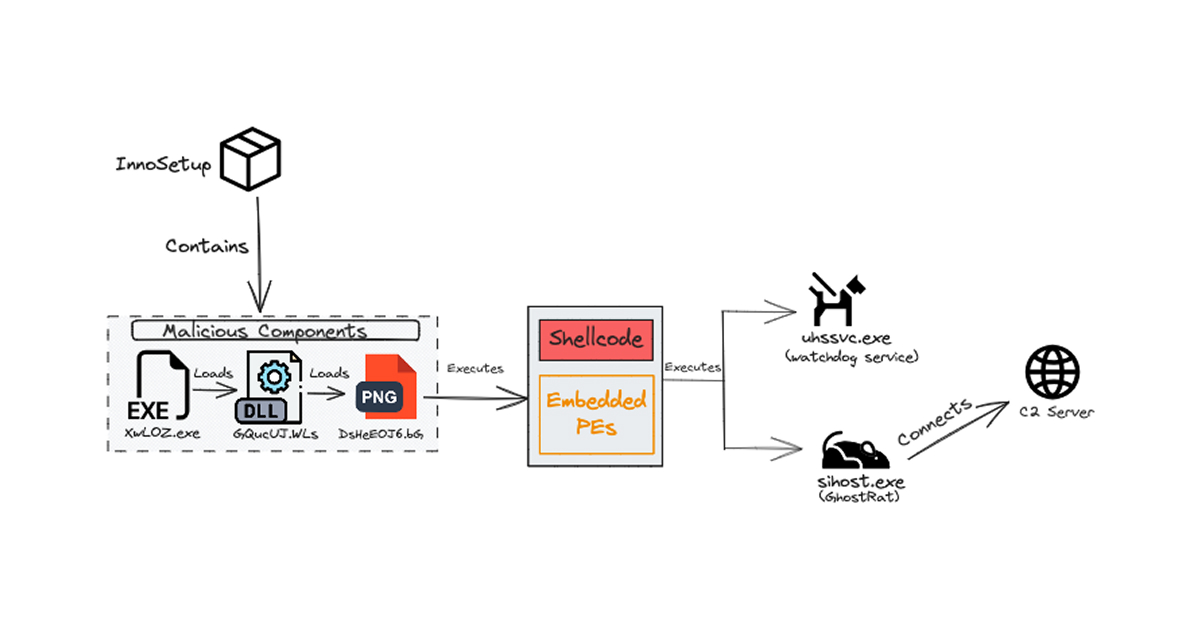
Despite law enforcement arrests targeting the Silver Fox threat group in mid-June 2026, its malware delivery network remains active as a Malware-as-a-Service (MaaS) platform. Affiliates continue to deploy hundreds of new typosquatted domains and exploit major cloud services to distribute an obfuscated Gh0stRAT variant.

2026-08-19
SecuritySnacks
Cybersecurity Reading List - Week of 2026-08-17
2026-08-17
SecuritySnacks
SecuritySnack - Account Farmers and Sellers

The underground market for farmed and stolen accounts is booming—driven by lax signup security and corporate pressure to show user growth. In this SecuritySnack, DTI investigates active account reselling marketplaces, examines SEC regulatory risks, and shares actionable steps for fraud teams to detect and block synthetic accounts.

2026-08-03
Newsletters
Twenty Flight Newsletter

August has come and gone, and my team and I have finally recovered from the excessive Las Vegas heat we had to endure during Hacker Summer Camp. However, August ending in Seattle also means we have roughly only six more weeks before the sun takes a break from the Pacific Northwest, and the eternal gray sets in until next April. And let’s be real, that six week estimation is a generous one - Take your vitamin D supplements, people! While the sun may be setting earlier, the threats have been shining plenty bright to keep my team busy.

Learn More
2026-09-17
Newsletters
Hey Nineteen (Newsletters)

Heatwaves in Vegas, high AQI in Seattle, and fresh threat research. Inside this edition: Iran’s growing hacktivist network, Mexican document scarcity scams, and the layered crypto architecture powering IRGC financial transfers.

Learn More
2026-08-14
Podcast episodes
How Russian Disinformation Campaigns Exploit Domain Registrars and AI
The Breaking Badness Cybersecurity Podcast discusses research from the DomainTools Investigations team on Russian Disinformation
Learn More
2025-04-16
Podcast episodes
Book Club with Dmitri Alperovitch
Discussing Dmitri's new book, World on the Brink: How America Can Beat China in the Race for the 21st Century.
Learn More
2024-05-01

Research

View All
Research
Lemmings: Russian Industrialized Persona Provisioning and Management for Active Measures Campaigns

Leaked internal data from Russian contractor Okenit reveals "Lemmings" (Лемминги)—a Python-based framework designed to industrialize the creation, verification, and management of synthetic online personas for Russian active measures. Built to automate phone verification, email infrastructure, CAPTCHA solving, and anti-detection measures, Lemmings functions as the identity-provisioning layer within a larger ecosystem alongside proxy and tasking tools (SOI and SOS). Live tests against platforms like VK and Reddit demonstrate a shift toward scalable, modular software frameworks capable of maintaining durable cover identities for intelligence, influence, and disinformation operations.
Learn More
Research
Threat Intelligence Report: University Leak Exposes Russia’s Military Cyber Training Pipeline

A leaked cache of institutional files reveals that Department No. 4 at Bauman Moscow State Technical University operates as a structured force-generation pipeline for Russian military cyber operations, training roughly 250 students across specializations. Supervised directly by senior GRU leadership, the program blends offensive intrusion, malware analysis, financial-systems targeting, and cryptographic defense with field placements that feed graduates straight into GRU- linked cyber formations like APT28 (Unit 26165) and Sandworm (Unit 74455).

Learn More
Research
Chinese Malware Delivery Domains Part V

Despite law enforcement arrests targeting the Silver Fox threat group in mid-June 2026, its malware delivery network remains active as a Malware-as-a-Service (MaaS) platform. Affiliates continue to deploy hundreds of new typosquatted domains and exploit major cloud services to distribute an obfuscated Gh0stRAT variant.

Learn More

SecuritySnacks

View All
SecuritySnacks
SecuritySnack - Account Farmers and Sellers

The underground market for farmed and stolen accounts is booming—driven by lax signup security and corporate pressure to show user growth. In this SecuritySnack, DTI investigates active account reselling marketplaces, examines SEC regulatory risks, and shares actionable steps for fraud teams to detect and block synthetic accounts.

Learn More
SecuritySnacks
Scarcity Scams

When government backlogs trigger appointment scarcity, scammers step in.This investigation exposes the mechanics of "scarcity scams"—from replica portals to weaponized session-recording tools. Discover how cybercriminals exploit administrative bottlenecks globally to extract fake fees and harvest critical identity data.

Learn More

Newsletters

View All
Newsletters
Twenty Flight Newsletter

August has come and gone, and my team and I have finally recovered from the excessive Las Vegas heat we had to endure during Hacker Summer Camp. However, August ending in Seattle also means we have roughly only six more weeks before the sun takes a break from the Pacific Northwest, and the eternal gray sets in until next April. And let’s be real, that six week estimation is a generous one - Take your vitamin D supplements, people! While the sun may be setting earlier, the threats have been shining plenty bright to keep my team busy.

Learn More
Newsletters
Hey Nineteen (Newsletters)

Heatwaves in Vegas, high AQI in Seattle, and fresh threat research. Inside this edition: Iran’s growing hacktivist network, Mexican document scarcity scams, and the layered crypto architecture powering IRGC financial transfers.

Learn More
Newsletters
Eighteen Newsletters and a Dozen Roses

June’s roundup of research - from cyberattacks on water infrastructure OT and ICS to DNS hijacking and an AiTM campaign targeting Microsoft365 users. 

Learn More