Ever think about the duality of fishing and hunting? Folks may argue fishing is a more passive endeavor. One sets a lure and waits. Hunting on the other hand, folks may argue, is a more active endeavor in which a hunter might generally be expected to seek out their intended target.
Let’s put this in terms of cyber threats. Most humans by now have undoubtedly heard of cyber attacks and perhaps even had some experiences with phishing in its various forms be it over email, text, voice call or a discord channel. But, what about the threat hunters? Threat hunting proactively seeks out undetected threats, usually within an organization’s network. Investigating indicators in a threat report can identify suspicious domains, detect patterns, and correlate findings with other sources.
With that said, thousands upon thousands of ill-intent domains are registered every day and some few fine folks set out the hounds and have a proper hunt. As one does, the trails are scoured and more indicators are found. But without further ado, this is one such quarry.
Opening Meet
This hunt got its start from a CloudFlare report on SloppyLemming. Also known as Outrider Tiger, SloppyLemming has reportedly been targeting Pakistani entities among others in Southeast Asia since late 2022. A range of domains have been utilized to lure victims into credential harvesting sites and deliver malware.
Frequent Domain Registration Patterns
- Use of CloudFlare services
- 90 day SSL Certificates
- Trends in domain naming convention
- Frequently assessed with risk scores of 100 by DomainTools
There’s the scent and the hunt begins. Sifting through domain registrations, DNS records, web scan data and the like, the lines form.
Hunting For Associated Indicators:
SloppyLemming domain `aljazeerak[.]online`
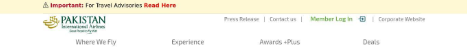
Website Title `Pakistan International Airlines - PIA | Great People to Fly With`
-> Unreported domain `fly-pakistan[.]com`
Historic Screenshot of domain aljazeerak[.]online masquerading as a Pakistani Airline
SloppyLemming domain `itsupport-gov[.]com`
whois email `abdulrehm8282[@]gmail[.]com`
-> Unreported domain `itsupport-gov[.]net`
- SSL temok[.]com + MX eye-mail[.]net + Registrar NameSilo
- Has Google Code `G-5XJE64N2SQ`
SloppyLemming domains `cflayerprotection[.]com, cloudlflares[.]com`
Whois Email `cht8p9zpl5[@]domprivacy[.]de`
-> Unreported domains
mfaturk[.]com
firebasebackups[.]com
cloudproxyserv[.]com
Historic Screenshot of domain paknavy-pk[.]org

Hunting CloudFlare Worker With SubDomain Name Masquaredes in DNS Records
Next, we search for CloudFlare Workers[.]dev subdomains with navy or gov and pk or lk naming elements using DNSDB Scout
;; query: Regex RRNames (navy|gov)-(pk|lk).+workers\.dev\.$ ANY (Limit 5000) // Last After: 2024-09-26 00:00:00 (UTC)
Sample:
```
anfbalochistan-gov-pk.workers[.]dev
clickonce.pakistan-gov-pk.workers[.]dev
cpanel-nha-gov-pk.pakistan-gov-pk.workers[.]dev
discordoutput.pakistan-gov-pk.workers[.]dev
email-moitt-gov-pk.pakistan-gov-pk.workers[.]dev
fbr-gov-pk-auth.workers[.]dev
gda-gov-pk.kr-i-sas-orv-e-l-a.workers[.]dev
gov-pk.workers[.]dev
gov-pkgov.workers[.]dev
gwadarport-gov-pk.gwadarportt.workers[.]dev
helpdesk-police-gov-pk.aabhimulla446.workers[.]dev
instagram-com.pakistan-gov-pk.workers[.]dev
ispr-gov-pk.workers[.]dev
kpt-gov-pk.workers[.]dev
maif-piac-aero.gov-pkgov.workers[.]dev
mail-asian-parliament-org.pakistan-gov-pk.workers[.]dev
mail-communication-gov-pk.pakistan-gov-pk.workers[.]dev
mail-depo-gov-pk.govtpak.workers[.]dev
mail-depo-gov-pk.ntc-telecomcorporation.workers[.]dev
mail-dgdp-gov-pk.ntc-telecomcorporation.workers[.]dev
mail-ecac-gov-pk.pakistan-gov-pk.workers[.]dev
mail-ecp-gov-pk.ntc-telecomcorporation.workers[.]dev
mail-ecp-gov-pk.pakistan-gov-pk.workers[.]dev
mail-fbr.gov-pk.workers[.]dev
mail-gwadarport-gov-pk.kr-i-sas-orv-e-l-a.workers[.]dev
mail-gwadarport-gov-pk.ntc-telecomcorporation.workers[.]dev
mail-hit-gov-pk.ntc-telecomcorporation.workers[.]dev
mail-invest-gov-pk.gwadarportt.workers[.]dev
mail-islamabadpolice-gov-pk.ntc-telecommunication-safecity.workers[.]dev
mail-kpt-gov-pk.gob-pk.workers[.]dev
mail-kpt-gov-pk.niancao010.workers[.]dev
mail-kpt-gov-pk.pak-gov-pk.workers[.]dev
mail-mod-gov-pk.pakistan-gov-pk.workers[.]dev
mail-modp.gov-pkgov.workers[.]dev
mail-modp-gov-pk.govtpak.workers[.]dev
mail-modp-gov-pk.ntc-telecomcorporation.workers[.]dev
mail-modp-gov-pk.pak-gov-pk.workers[.]dev
mail-mofa-gov-pk.pakistan-gov-pk.workers[.]dev
mail-na-gov-pk.na-gov-pk.workers[.]dev
mail-nba-gov-pk.pakistan-gov-pk.workers[.]dev
mail-ntc-net-pk.gov-pkgov.workers[.]dev
mail-paf-gov-pk.ntc-telecomcorporation.workers[.]dev
mail-paknavy.gov-pk.workers[.]dev
mail-pc-gov-pk-login.ethanhunthero125.workers[.]dev
mail-pof-gov-pk.govtpak.workers[.]dev
mail-ppra-org-pk.pakistan-gov-pk.workers[.]dev
mail-punjab-gov-pk.ntc-telecomcorporation.workers[.]dev
mail-punjab-gov-pk.ntc-telecommunication-safecity.workers[.]dev
mail-punjab-gov-pk.punjab-info-tech-board.workers[.]dev
mail-sco-gov-pk.mil-bd.workers[.]dev
mail-sco-gov-pk.ntc-telecomcorporation.workers[.]dev
meharusman524gov-pk.workers[.]dev
meharusman524gov-pk4230.workers[.]dev
na-gov-pk.workers[.]dev
na-gov-pk-bfd.workers[.]dev
navy-lk.workers[.]dev
nha-gov-pk.pakistan-gov-pk.workers[.]dev
old-violet-aae5.meharusman524gov-pk4230.workers[.]dev
pak-gov-pk.workers[.]dev
pakistan-gov-pk.workers[.]dev
paknavy-gov-pk.workers[.]dev
pitb.gov-pkgov.workers[.]dev
pitb-gov-pk.workers[.]dev
pmo-gov-pk-auth.workers[.]dev
pof-gov-pk.workers[.]dev
pythonscanner.gov-pkgov.workers[.]dev
reports-ecp-gov-pk.mlc-landdistribution.workers[.]dev
throbbing-sun-f4e8.meharusman524gov-pk4230.workers[.]dev
wapda-gov-pk.workers[.]dev
webmail.wapda-gov-pk.workers[.]dev
webmail-gda-gov-pk.gwadarportt.workers[.]dev
webmail-wapda-gov-pk.pakistan-gov-pk.workers[.]dev
worker-cool-credit-6d6f.navy-lk.workers[.]dev
worker-dark-paper-2231.gov-pkgov.workers[.]dev
worker-patient-wave-96d1.pakistan-gov-pk.workers[.]dev
worker-plain-wind-01a9.pakistan-gov-pk.workers[.]dev
worker-silent-pond-c90d.pakistan-gov-pk.workers[.]dev
```

- Site content of domain `pythonscanner.gov-pkgov.workers[.]dev`
Hunting for Domain Masquerades in Whois and Web Scans
Hunting for Pakistani domain masquerades using cloudflare. The nature of these broader hunts are apt to uncover unintended prey. In this case, the stumbling on a mix of Pakistani travel and government job boards, and Crypto exchange masquerades.
```
govtjobspak[.]live
pakkjob[.]com
pakgovtsjobs[.]com
gov-declare[.]help
karakfinance[.]cfd
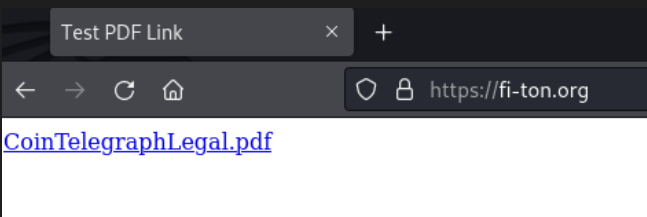
fi-ton[.]org
```


```
search:query=CoinTelegraphLegal.pdf&crumb=location:\\45.82.13[.]15@80\Downloads\&displayname=Downloads
```
Conclusion
Hunting for undetected threats can take on many forms. Prompted by threat reports and intelligence, threat hunters may cast a wider net to seek out undetected indicators, detect patterns, and correlate findings with other sources of information. That said, wider nets can catch more than the intended quarry. In this case, finding an ecosystem of websites impersonating as Pakistani airlines, government job boards, as well as remnants of malicious domains and scanners on Pakistani government domains. While it may not all be SloppyLemming activity, it highlights an apparent wider spread targeting of Pakistan.