Executive Summary
Online personas calling themselves MrHex, @Mr8ex, MrDarkRoot, and Darku3er, have been creating and advertising domains on the darknet and clearnet. These personas and their created domains form a hack-and-leak ecosystem that has evolved from commercial data brokerage into politically motivated disclosure activity and cyber-physical operations on behalf of Iran.
The group has a strong Iran connection including use of hosting in Iran. Persian-language news reporting has described MrHex as an Iranian cyber actor, and their targets have featured entities in Israel and the U.S., Kurdish opposition entities, and security organizations deemed enemies of Iran. The actors have also referred to Handala as their "brothers."
In a September 30, 2026 forum post, MrDarkRoot claimed that Handala provided information on Israeli and U.S. targets for the group to redistribute. Some of the same material later appeared on MrHex’s site, mrhex[.]sbs, and BlackLeaks[.]sbs sites. This suggests Handala may have originally provided stolen information that MrHex then published. Since the sites came online however, MrHex has expanded his activities to encompass IT and OT hacking and threats of more to come.
In September 2026, MrHex claimed attacks against U.S. industrial systems, including chemical-injection, natural-gas, and crude-oil facilities. These claims remain largely unverified, but evidence in video and screen grabs lend credibility to some of the claims. However, no independent evidence has been identified confirming that the group caused contamination, explosions, or other physical damage. This change in operations infers a more active relationship with, or direction by, Handala as they have evolved their TTP’s to include attacks on infrastructure systems as well.
In early October 2026, changes to the campaign began to appear. On DarkForums, MrDarkZRoot began a new campaign of data sales of American companies and government data they claimed they had hacked. In these posts, they created new Telegram channels for sales and leaks. This is a change in cadence and means of communication that appears to be in response to the MrHex sites being taken down by unknown forces. The domains were not seized, but the sites are completely down as of this writing, October 20th 2026.
Overall, MrHex is best assessed as an Iran-aligned hack-and-leak operation with access to stolen information in cooperation with Handala, and recently has added credible evidence of at least one industrial-control-system compromise. If the OT access is proven to have been real world access, and not just disinformation for effect tied directly to Handala-associated actors, it would represent a notable change in tradecraft from their previously-observed emphasis on data theft, leaks, and doxxing aligning with Handala and Cyberav3ngers.
Timeline
The timeline below illustrates the evolution of the MrHex ecosystem from a relatively small data marketplace into a coordinated multi-platform operation involving the sale, publication, and redistribution of allegedly compromised information.
Beginning with the establishment of a site, JokerData[.]org, the infrastructure in December 2025 gradually expanded to include dedicated bulk-download repositories, searchable databases, and Telegram distribution channels. By August 2026, the actors were actively promoting military and government-related datasets for download as action against the enemies of Iran. By September, increasingly aggressive claims involving unauthorized access to U.S. industrial control systems and critical infrastructure were being advertised in news sources.
During this same period, the emergence of additional actor identities and public acknowledgment of cooperation with Handala suggested an expanding network of individuals involved in acquiring, marketing, and distributing stolen information. Collectively, these developments indicate a shift toward a more organized hack-and-leak ecosystem that combines commercial data trafficking with politically motivated messaging and influence operations.
- December 23, 2025: jokerdata[.]org was registered, marking the earliest identified infrastructure associated with the MrHex ecosystem.
- December 29, 2025: jokerdata.shop was registered, expanding the JokerData infrastructure used to advertise and distribute compromised data.
- June 1, 2026: blackleaks.sbs was registered, adding a bulk data distribution platform to the ecosystem.
- July 31, 2026: mrhex.sbs was registered, establishing a searchable portal for compromised data and public-facing leak operations.
- August 27, 2026: MrDarkRoot publicly advertised military data from multiple countries, directing prospective buyers to @MrhexStore, @Darku3er, and mrhex.sbs.
- September 18, 2026: A screen recording surfaced showing access to an industrial HMI associated with Station Verdad, displaying @Mr8ex and MrHex branding.
- September 19, 2026: Persian-language media repeated claims of cyberattacks against industrial facilities in Knoxville, Granite City, and East Ridge. These incidents remained unverified.
- Late September 2026: @mrhexTeam emerged as a major dissemination channel, promoting large data archives involving prominent Israeli figures through actor-linked websites.
- September 30, 2026: MrDarkRoot publicly acknowledged receiving information from Handala for redistribution through the network, providing further evidence of cooperation between the actors.
- Early October 2026: mrhex.sbs continued expanding its searchable databases, publishing records purportedly associated with U.S. and Israeli military personnel, law enforcement, intelligence agencies, and political figures.
Personas and Brand Structure
MrHex
MrHex is the principal public-facing identity of the current campaign. The mrhex[.]sbs site describes itself as an “Organizational disclosure” platform developed by MrHex and hosts structured collections of data labeled:
- U.S. Army
- U.S. Police
- FBI/CIA
- Israeli police
- Individual archives for senior Israeli and U.S. figures
The content includes previously hacked dumps of email spools from Benny Gantz, Ehud Barak, Gabi Ashkenazi, Ron Prosor, and Kash Patel. All of these are dumps previously leaked by Handala and CyberAv3ngers.
Visible record counts include
- 8,059 U.S. Army records
- 9,310 U.S. police records
- 108 purported FBI/CIA records
- 38,765 Israeli police records
The sites are more than a conventional static leak page; their structure suggests that source material is being parsed, categorized, indexed, and presented through database-backed collections of previous and newly acquired data. This makes MrHex function as a data leak platform rather than simply a file-hosting ecosystem, and aligns with the established pattern of Iranian information operations carried out by MOIS.
@Mr8ex
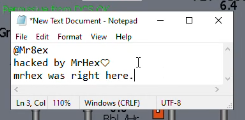
The personna @Mr8ex should be treated as a confirmed alternate handle for the MrHex persona. The strongest evidence comes from the September 18 industrial-system recording where the handle appears directly within the compromised environment on video. At the same time, the same named Mr8ex Telegram address was independently promoted in Persian-language news sources as the Telegram contact for MrHex. The Telegram account remains active as a direct-contact identity rather than a public broadcast channel, suggesting that @Mr8ex serves as a lower-visibility operational or communication handle while MrHex functions as the public-facing brand.
MrDarkRoot
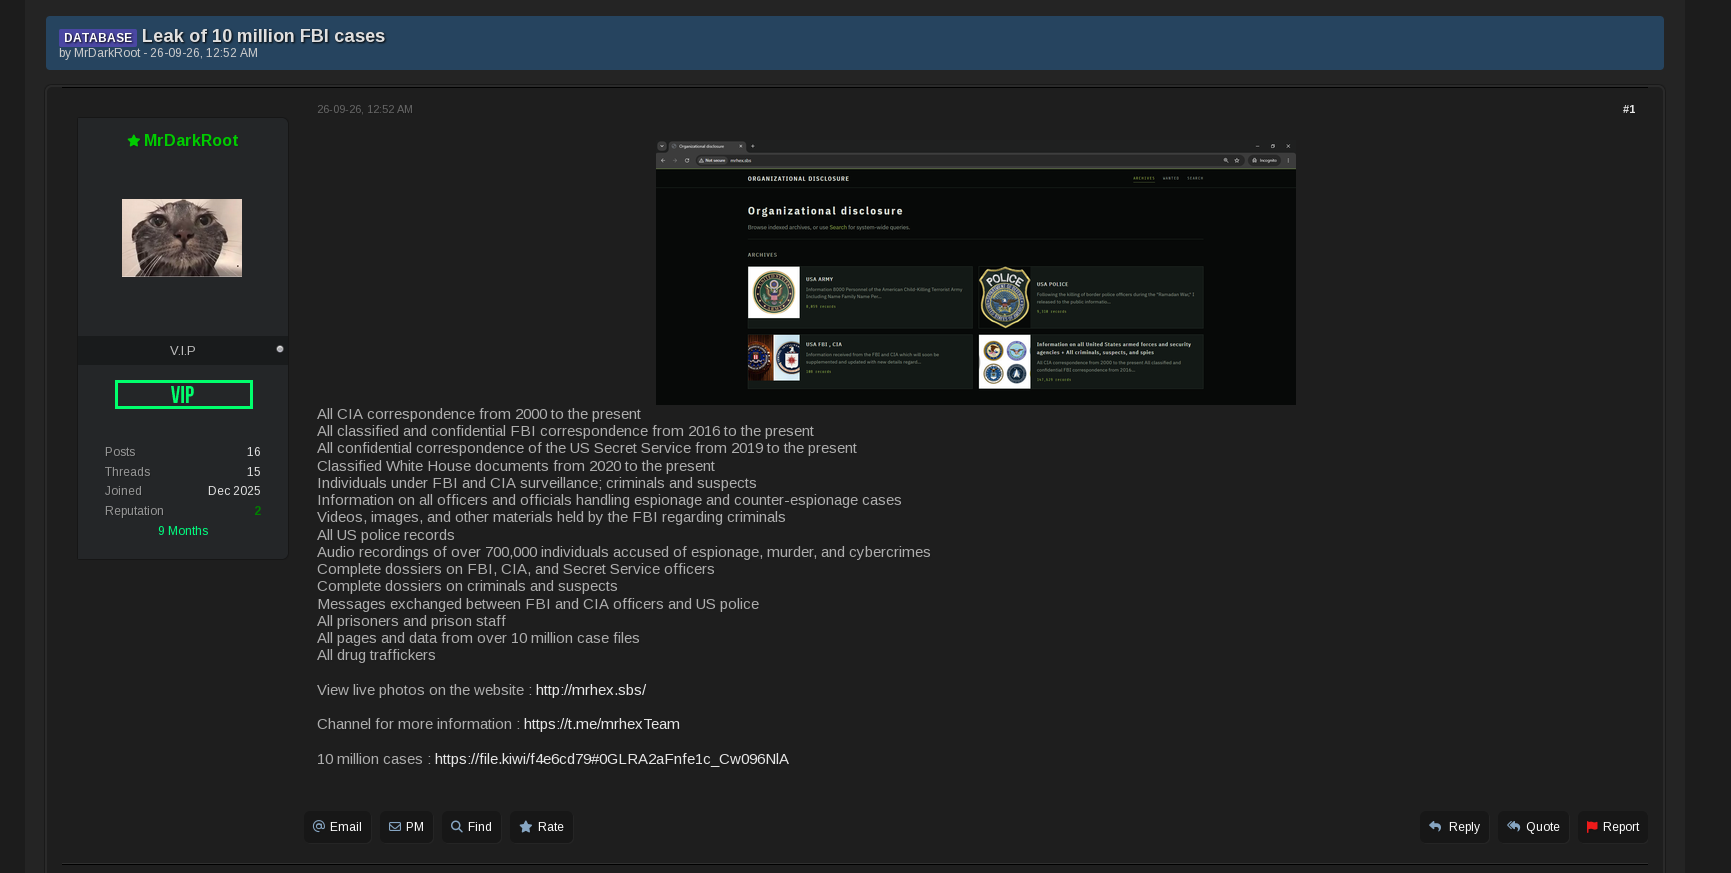
MrDarkRoot functions primarily as the marketplace-facing identity for the campaign. In an August DarkForums post, the account advertised an updated military-data collection covering military and other forces in more than 14 countries and offered the dataset for $10,000. Interested buyers were directed to the telegram channels @MrhexStore, @Darku3er, as well as the domain mrhex[.]sbs for additional samples. This establishes a direct operational connection between MrDarkRoot and the broader MrHex network rather than a simple similarity in naming.
Separate monitoring also found MrDarkRoot advertising numerous alleged education-sector datasets during August 2026, reinforcing the assessment that the account serves as a data-brokerage and sales interface, although many of the claimed breaches remain independently unverified.
In recent activity on the Darkforums groups, MrDarkRoot has shown they are moving between data sales and activities in support of Iran again. Within the span of a week, the account posted four new posts offering American data for sale and leaks in support of Iran by leaking data to the MrHex website.

On October 7th 2026, MrDarkRoot posted that they had hacked a number of American government sites and were offering 200 gigabytes of data for $10,800.00. This data could also be broken down to individual data from sites as well instead of a lump sum. They list the MrHex Store Telegram channel for the sales.
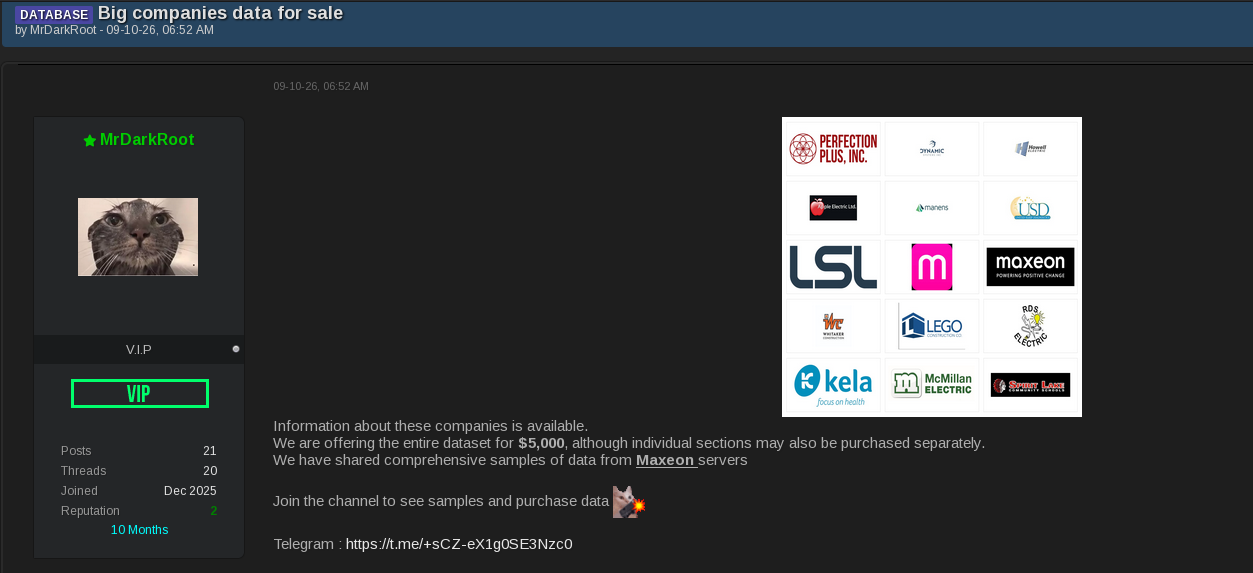
On October 9th 2026, on DarforumsRU, the account, the MrDarkRoot account posted a new claim that they had hacked a large number of corporations online. They also referenced a new channel (MrHexStore) on Telegram to access and offer payment for the data. In total, they are offering the whole dataset, which they do not list the entire amount of data that they claim to have, for $5000.00.
On October 10th 2026, MrDarkRoot posted sales of company data for a large number of companies that they claimed to have hacked. These are American companies and are on offer for $1000.00 per the post with a link to the Telegram channel (MrHexStore)
On October 11th 2026, MrDarkRoot then posted that they had previously sold Israeli data now on offer for free on the newly created IRGCIntelligence Telegram channel.
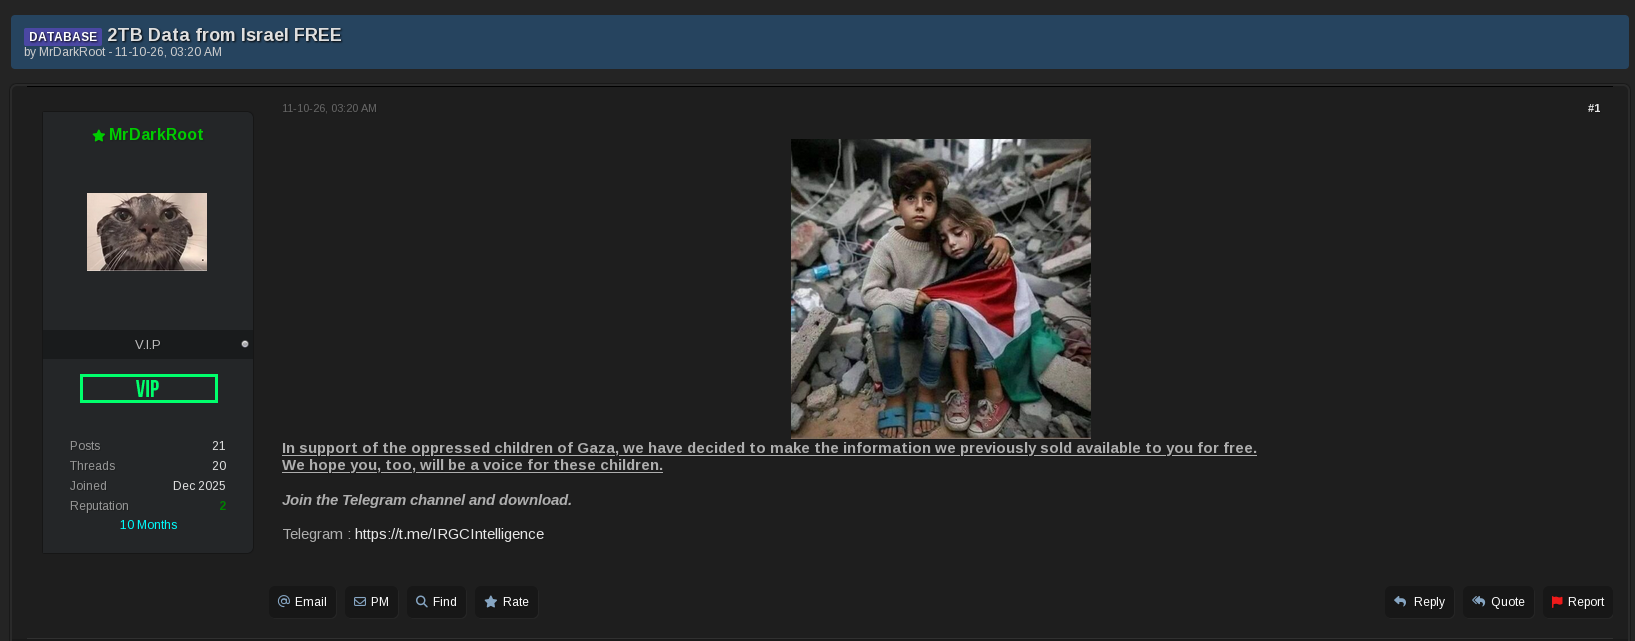
While it seems that their activity is ramping up, it is unclear as to what the goal is other than perhaps as a means of propaganda or psychological operations motives. As the data has yet to be downloaded and investigated by anyone, this all could just be previously leaked data or, truly hacked information of unknown origins and import.
@Darku3er
Darku3er appears to serve as the transactional contact within the campaign. DarkForums sales posts specifically directed prospective buyers to the telegram account @Darku3er to purchase advertised datasets, indicating a functional role in handling buyer communications and transactions. The available evidence suggests a basic division of responsibilities in which MrDarkRoot handles advertising and marketplace reputation. Darku3er manages buyer interaction, and MrHex provides samples and public distribution in theory. It remains unclear whether Darku3er is a separate operator or simply a compartmented account controlled by the same individual or group.
Campaign Website Infrastructure
The MrHex campaign relies on a small but distinct set of websites that appear to have evolved alongside the actor's operational needs. The earliest identified site, JokerData, was used primarily to advertise and sell access to stolen datasets. This was followed by BlackLeaks, which provided a simple bulk-download function for documents and email archives, and later by mrhex[.]sbs, which introduced a more polished, searchable interface for presenting and organizing victim data.
Taken together, the sites show a progression from basic data sales and file hosting toward a more structured leak and influence platform. Shared infrastructure, overlapping victim material, common actor promotion, and complementary roles across the domains support that they are part of the same administrative ecosystem or are operated by actors working in close coordination.
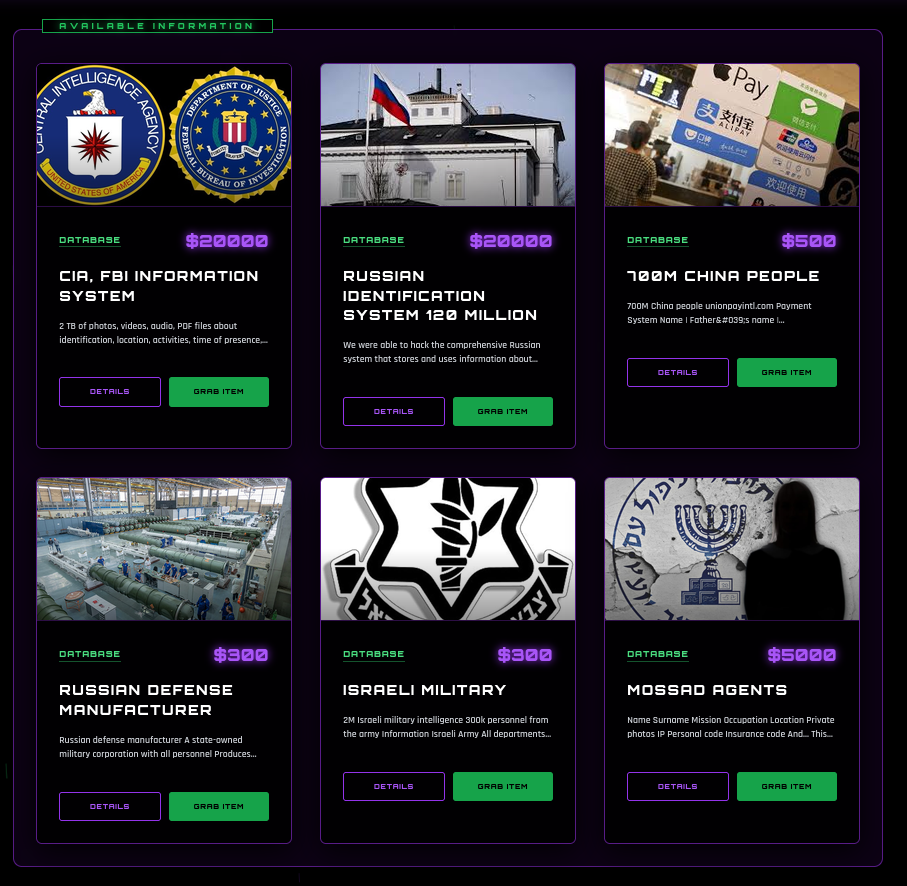
JokerData represents the earliest identified infrastructure layer associated within the website campaigns. IRIS domain data shows that jokerdata[.]org was registered on December 23, 2025 followed by jokerdata[.]shop on December 29th. This placed both domains being created and used before the blackleaks[.]sbs and mrhex[.]sbs sites were stood up.
Jokerdata[.]org was hosted through OVH at 51.79.96.115. However, its Name Server and SOA records referenced ParsVDS, with Iranian hosting company infrastructure tying them directly to Iran.
The infrastructure associated with jokerdata.shop provides a meaningful technical connection to Iran. IRIS records show that the domain's mail service resolves to 185.208.173.17, an address announced by AS202269, BitCommand LLC. That same infrastructure is used by Iranian .ir domains configured with ParsPack nameservers. Other AS202269 prefixes are directly associated with ParsPack and Iranian network resources registered in Tehran. This does not prove that the operators are physically located in Iran or directly controlled by the Iranian government, but it adds an independent infrastructure-level Iran nexus that reinforces the broader pattern of pro-Iran messaging aligned with Iranian strategic interests.
Both sites were more polished and resembled other sites using the “Joker” moniker in the past that sold swaths of data stolen from various governmental and private companies. These sites were online only briefly, and as such, were only copied by The Wayback Machine as initial landing pages. There is no other information as to whether or not any sales were made, and no news sources could be located on these sites.
BlackLeaks[.]sbs
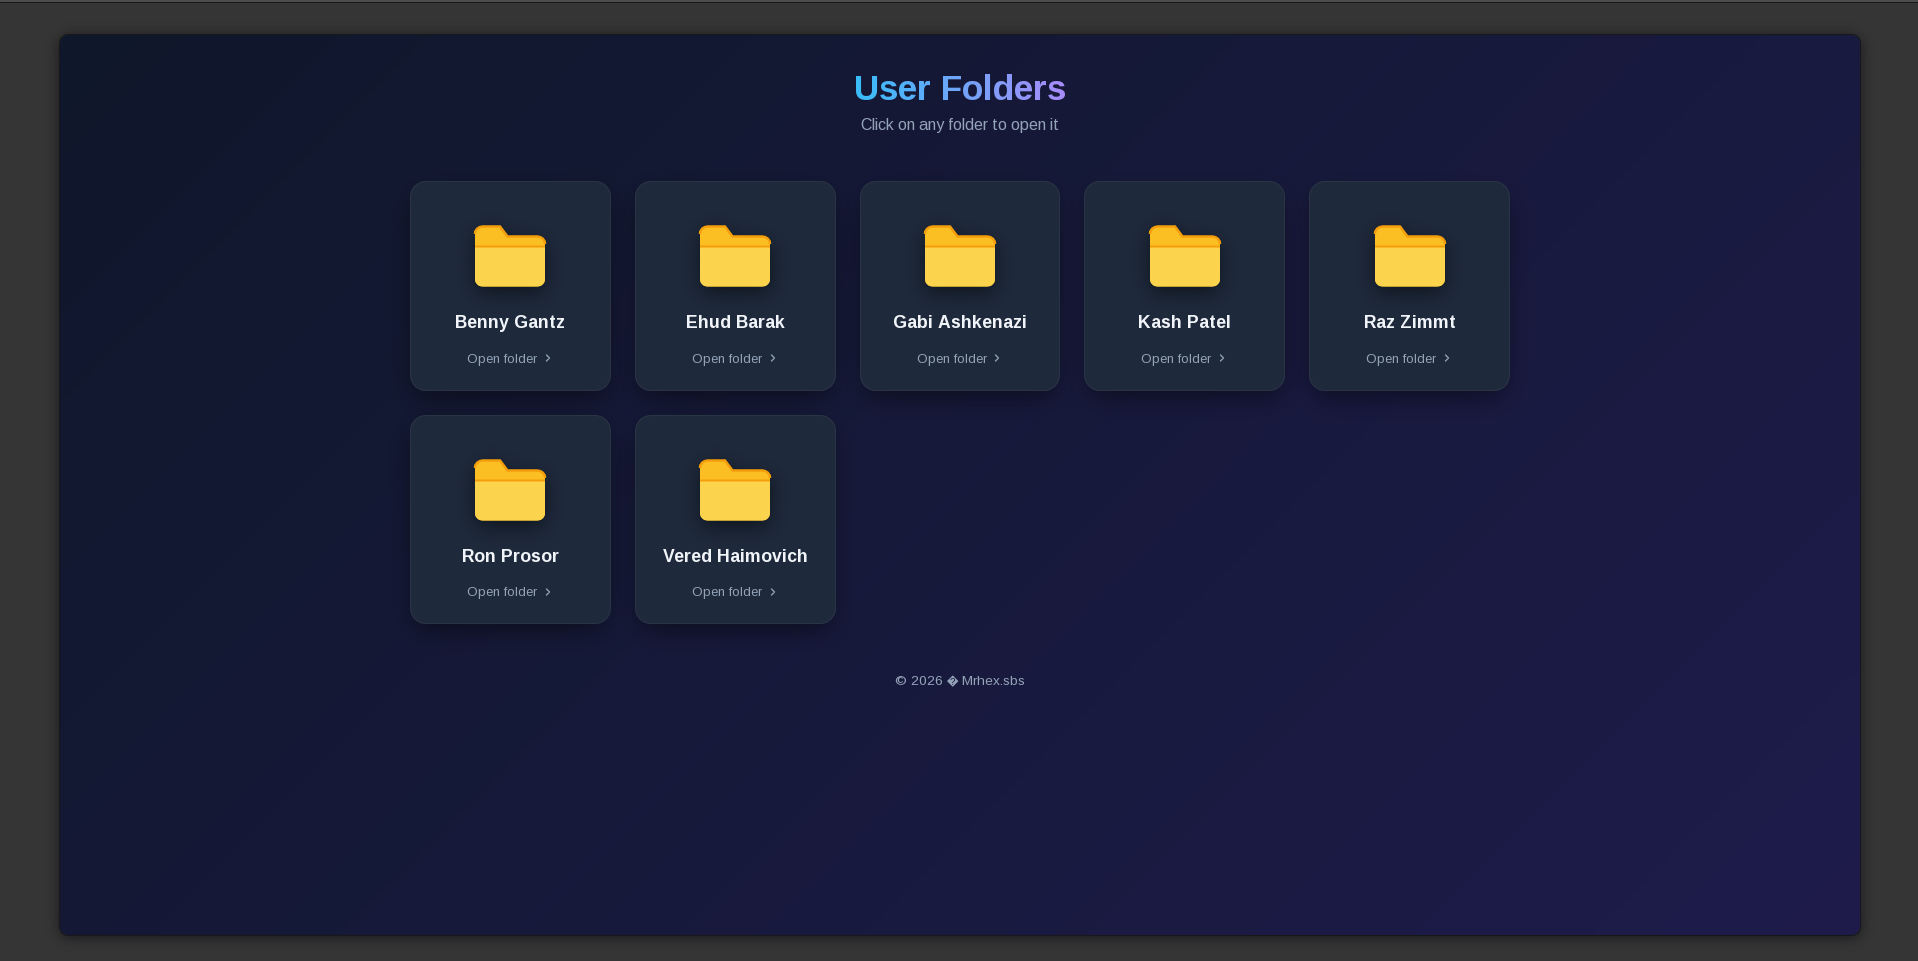
Blackleaks[.]sbs was registered on June 1, 2026, about two months before mrhex[.]sbs, and appears to serve as the campaigns early bulk-distribution platform for leaked documents, email archives, and other downloadable material. This site is a proto site and a backup for the more flashy mrhex[.]sbs site which is designed more for structured browsing, searching, and presenting individual records. This division suggests a deliberate separation between public-facing discovery on mrhex[.]sbs and large-scale file retrieval through blackleaks[.]sbs and external hosts.
MrHex[.]SBS
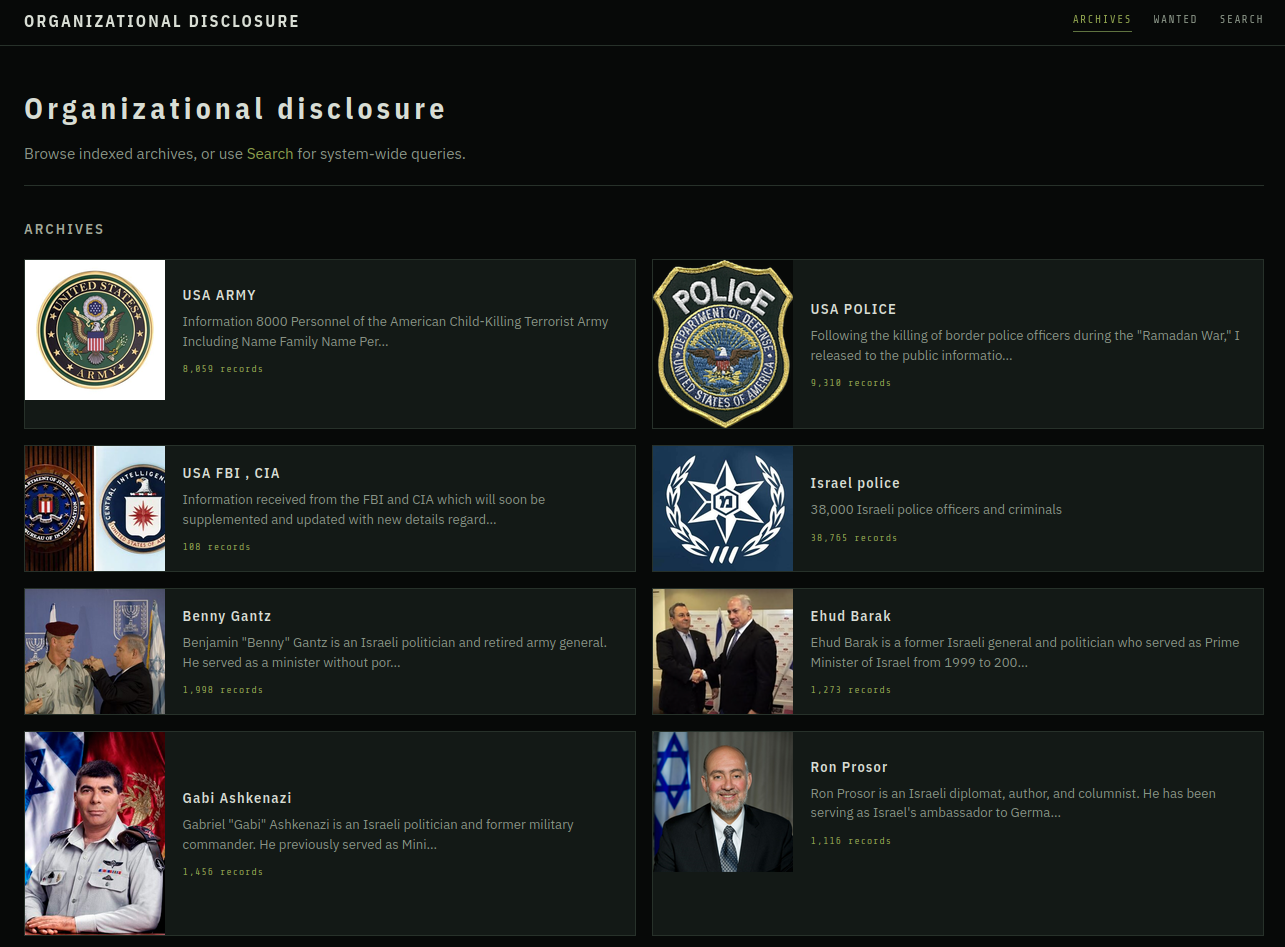
The MrHex persona’s newest site, MrHex[.]sbs (live September 24th 2026), claims it publishes a range of stolen data tied to government, military, law-enforcement, and political targets. The site’s second title is “Organizational Discloser” and attempts to emulate a Wikileaks style of hack and leak reporting. Its public archive includes collections labeled:
- U.S. Army
- U.S. Police
- FBI/CIA
- Israeli Police
- Benny Gantz (Israeli gov)
- Ehud Barak (Israeli gov)
- Gabi Ashkenazi (Israeli gov)
- Ron Prosor (Israeli gov)
- Kash Patel (FBI Director current)
These labels should not be treated as proof that all of the data came directly from the named organizations and as yet, primarily entail thumbnails of images of what seem to be ID cards and other snippets of screenshots. The only verified dumps are the email spools from earlier hacks carried out by CyberAveng3rs and Handala (Kash Patel, and the Israeli sets) which are available for download. Review of the purported FBI/CIA material, which presently consists only of thumbnails and names of individuals, has yet to have context other than what is being claimed by MrHex. Research has found that some names matched historical FBI personnel, while many others could not be independently linked to FBI or CIA employment.
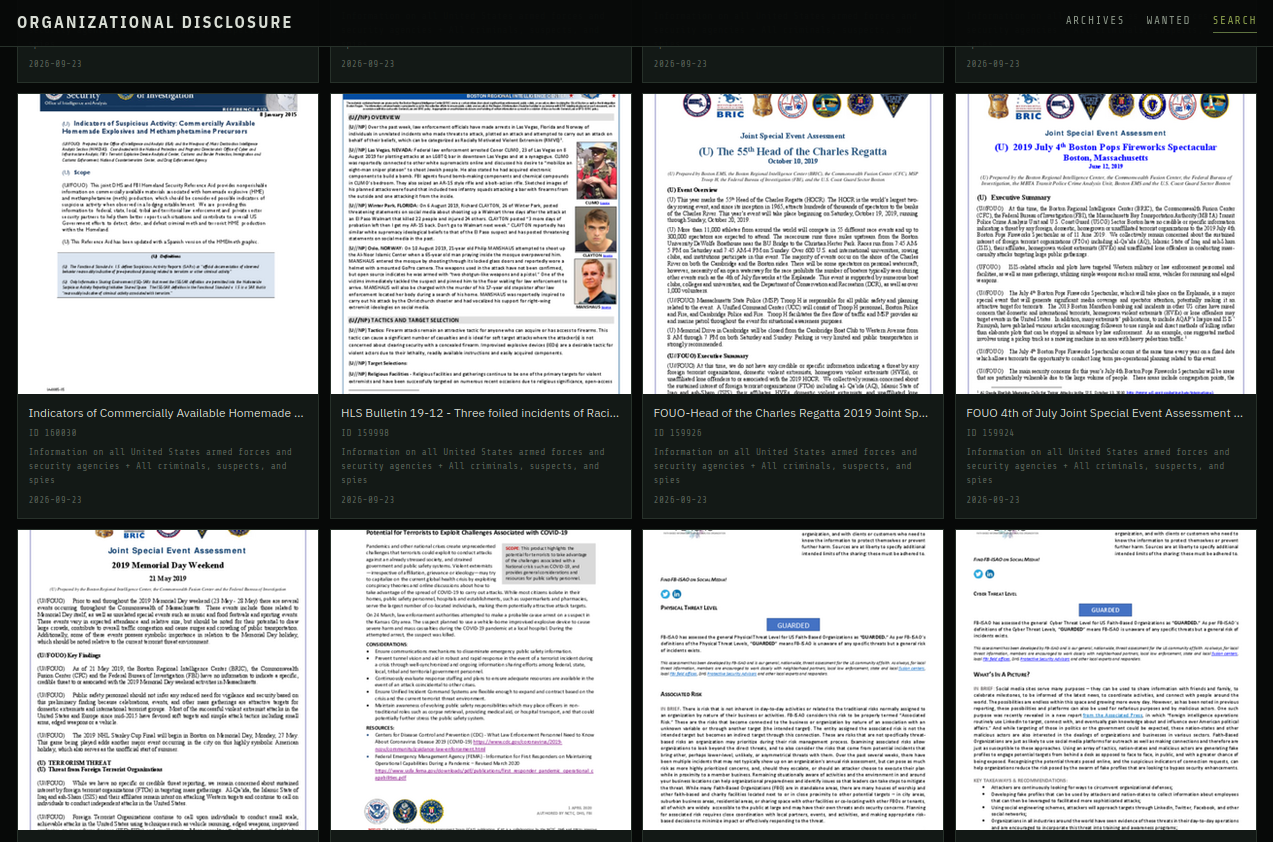
This suggests the archive may mix genuine breach data with scraped records, public information, older leaks, third-party collections, and mislabeled material. The likely value of the platform is therefore not just proving individual intrusions, but building a large searchable dataset that can support targeting, harassment, and future social-engineering activity.
It is also yet to be determined if the site’s owners’ claims are true that they have documents and other data that will be uploaded and put into searchable format using the site. At present, there is data in the form of images, but as the data is not provided en toto, these images cannot be assessed as anything more than an attempt to prove possession.
Sites Shared Infrastructure
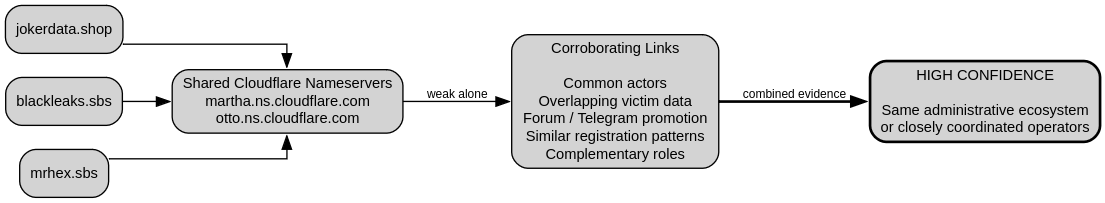
The domains jokerdata[.]shop, blackleaks[.]sbs, and mrhex[.]sbs were all observed using the same Cloudflare nameserver pair; martha.ns.cloudflare.com and otto.ns.cloudflare.com. Shared nameservers alone are weak evidence, but in this case they are supported by stronger links including common actors, overlapping victim data, and shared promotion across Telegram channels. These sites also have similar registration patterns and complementary operational roles. Taken together, along with the same actors linking them in their posts, these connections support a high confidence assessment that the three domains are part of the same administrative ecosystem operated by actors working in close coordination.

The way these sites are linked through actor-controlled advertisements also represents an evolution in tradecraft compared with earlier Handala campaigns. Handala has generally emphasized direct publication, ideological messaging, and release of stolen material through its own channels. In contrast, the MrHex ecosystem uses a more structured commercial-style workflow in which forum posts, Telegram accounts, sample sites, and bulk-download infrastructure are deliberately connected to move users through the campaign.
This approach resembles a marketplace and distribution network as much as a traditional hack-and-leak operation. The repeated cross-promotion of jokerdata[.]shop, blackleaks[.]sbs, and mrhex[.]sbs suggests a more mature effort to separate advertising, audience engagement, searchable presentation, and bulk delivery. If Handala-origin data is being fed into this system, the campaign reflects a shift away from simply leaking material toward packaging, indexing, marketing, and redistributing it through a persistent multi-platform ecosystem.
Tradecraft Evolution
The MrHex campaign's primary strength is the collection and amplification of stolen and embarrassing data aligning with Iranian information operations of the past. Its likely workflow is to acquire information, advertise the material through criminal forums, amplify it through Telegram and aligned media, and then use the information for political effect. The infrastructure appears divided around those roles:

This tradecraft has also evolved beyond simple data sales into influence activity. MrHex releases often combine genuine leaks, screenshots, or access with ideological messaging and claims of destructive impact. This allows the actor to use verified access as a foundation for more dramatic claims that may not be independently supported. The Station Verdad video is the clearest example: it credibly demonstrates unauthorized access to an industrial HMI, but it does not show pumps being disabled or industrial processes being manipulated. Subsequent reporting nevertheless framed the incident as a destructive attack. The result is a tradecraft modality in which demonstrated access can be amplified into claims of operational impact without showing the evidence needed to connect the two.
The MrHex campaign also uses the darknet as a means of propagation. Previous Handala campaigns used TOR (The Onion Router) sites , but this evolution seems to cut out having to have an onion address, eschewing the work of upkeep and security for the ease of posting data to known and highly trafficked darknet forums.
The Iran alignment is also increasingly integrated into this activity. Persian-language cybersecurity reporting has identified MrHex as Iranian and amplified its claims against U.S. infrastructure, while separate reporting links the actor to targets of direct Iranian security interest, including Kurdish organizations. The actors use pro-Iranian and anti-Israeli messaging, and MrDarkRoot has described Handala as its ideological “brothers.”
Taken together, this represents a shift from relatively straightforward data brokerage toward a broader model combining data exploitation, hack-and-leak activity, and politically aligned influence operations. The technical tradecraft remains comparatively simple, but the integration of these functions makes the campaign more effective and potentially more disruptive than a conventional leak site or data marketplace.
Critical Infrastructure Attack Claims
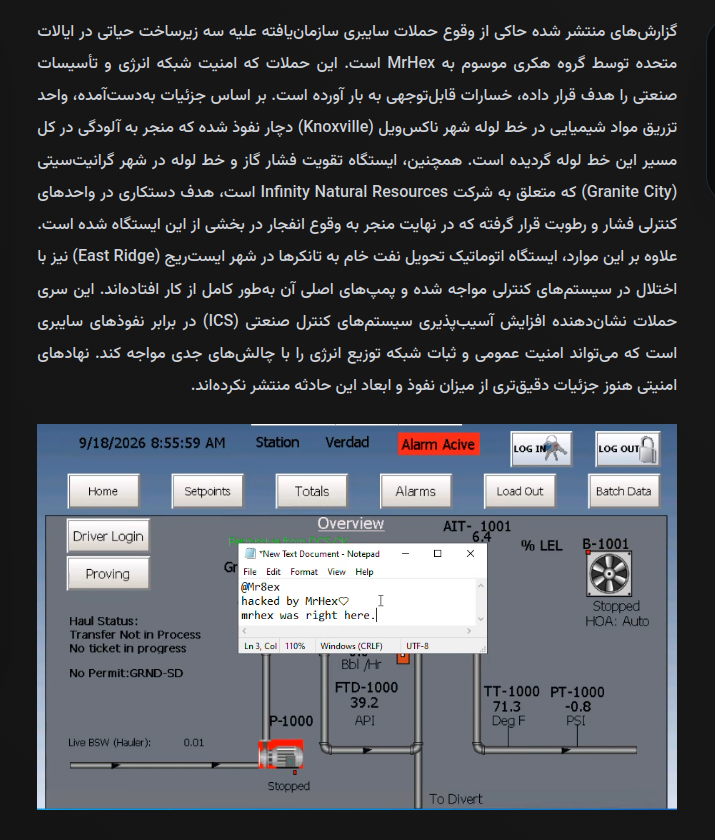
Published reports indicate that a hacker group known as "MrHex" has carried out organized cyberattacks against three critical infrastructure sites in the United States. These attacks, which targeted energy network security and industrial facilities, have caused significant damage. According to available details, a chemical injection unit on a pipeline in Knoxville was breached, resulting in contamination along the entire length of the pipeline. Additionally, a gas compressor station and pipeline in Granite City—owned by Infinity Natural Resources were subjected to tampering with pressure and humidity control units, ultimately triggering an explosion in part of the facility. Furthermore, an automated crude oil tanker loading station in East Ridge experienced control system disruptions that caused a complete failure of its main pumps. This series of attacks highlights the growing vulnerability of Industrial Control Systems (ICS) to cyber intrusions, posing serious challenges to public safety and the stability of energy distribution networks. Security agencies have not yet released further details regarding the extent of the breach or the full scope of the incident.
MrHex escalated their public messaging in September 2026 by claiming three successful attacks against U.S. industrial and transportation infrastructure. Persian-language reporting on September 19th described an alleged compromise involving a chemical-injection system in Knoxville TN, a gas-pressure facility in Granite City TN, and an automated crude-oil truck-loading station in East Ridge TN. The actor claimed these incidents caused pipeline contamination, an explosion, and disabled pumps. However, no matching incident has been independently identified through authorities, leaving the attack and the claims unverified.
The strongest technical evidence of genuine industrial access is a September 18 screen recording showing a Windows-based HMI labeled “Station Verdad.” The interface includes data consistent with a petroleum custody-transfer or truck-loadout environment. Batch records showing quantities of roughly 250 barrels further support that assessment. The footage provides credible evidence that the recorder had interactive access to a real industrial HMI rather than simply possessing screenshots. It does not, however, demonstrate destructive manipulation of those systems in the video.
Additionally, the claims of sites are confusing. The actor claims access to a system in Granite City TN, however, there is no such municipality in the US. The actor could have confused Tennessee with Illinois, but, even so, the video presented as proof of access, when looked at more carefully, has the word “Station Verdad” on the system. Investigation shows that there is a Verdad Resources LLC, in Colorado, that fits this naming scheme on the HMI however.
To date, there have been no statements of incidents for any systems involving the claims made in the video that Mr8ex has provided in this post online. In addition, the naming on the HMI console is inconclusive evidence of just what system it is, who owns it, or its location.
Overall, the available evidence supports credible unauthorized access to at least one industrial HMI, but does not demonstrate destructive OT capability. MrHex has shown that they can obtain or display access to industrial-control environments, but there is currently no verified evidence of altered control logic, changed safety settings, or physical damage directly attributable to the actor.
Conclusion
The MrHex Handala aligned campaign is best understood as an evolving hybrid between a criminal data market system, a hack-and-leak operation, and an emerging OT-access actor in service to Iran, affiliated with Handala and by proxy, Iran’s MOIS.
The infrastructure chronology suggests that this all evolved from JokerData, providing a commercial or data-broker foundation. This then evolved into BlackLeaks and added bulk dissemination via a simple file website. MrHex then emerged as the structured publication and ideological branding for a larger campaign that is still evolving. In this ecosystem, the MrDarkRoot brand markets material through criminal forums, Darku3er appears to handle transactions or direct contacts, and @Mr8ex acts as an alternate identity associated with the MrHex persona.
The relationship with Handala is credible enough to treat as a working intelligence judgment, but not as proof of common control. MrHex appears capable of receiving and republishing material associated with an established Iran-linked intrusion actor, substantially increasing its effective capability even if it did not perform the original compromises.
The most important recent development are the claimed OT attacks on infrastructure in the US. The September 18 recording provides credible evidence that MrHex or an associated operator had interactive access to a functioning petroleum HMI and potentially manipulated it.
At the same time, the evidence does not support the group's more dramatic claims of causing pipeline contamination, explosions, or pump failure. At least one claimed victim narrative overlaps with a genuine non-cyber industrial accident, increasing the possibility of conflation or embellishment.
The appropriate intelligence posture is therefore neither dismissal nor acceptance of actor claims at face value. MrHex should be considered a credible data-theft, leak-distribution, and unauthorized-access threat whose demonstrated access is narrower than its propaganda claims. Its relationships with data markets on the darknet and Handala materially increase its reach, while its recent industrial-system access indicates potential progression toward more consequential operational technology activity.