Where has this year gone?! We are six months into formally launching DomainTools Investigations (DTI) and subsequently this newsletter! If you’re a returning reader, I’m glad you keep coming back! If you’re a new reader, what you’re about to read is news from our group of researchers and analysts providing their expertise in investigating, mitigating, and preventing Domain and DNS based attacks.
Today, I had the opportunity to listen to a session at FIRSTCon25 where Tom Millar of CISA, Eireann Leverett of Killara Cyber, Wendy Nather of 1Password, and Declan Ingram of Trust Hound, discussed cyber resilience in the current threat context. One of the core focuses during this session was Community and how cyber resilience is born out of Community.
The message of Community resonated with me because of our work here with DTI and how great this Community has been through the years. So take a look around, and if you’d like to collaborate with us to get further in our analyses, please let us know.
So without further ado, here’s what our incredible team has been up to in June:
🐀 Trust Exploited: NetSupport RAT
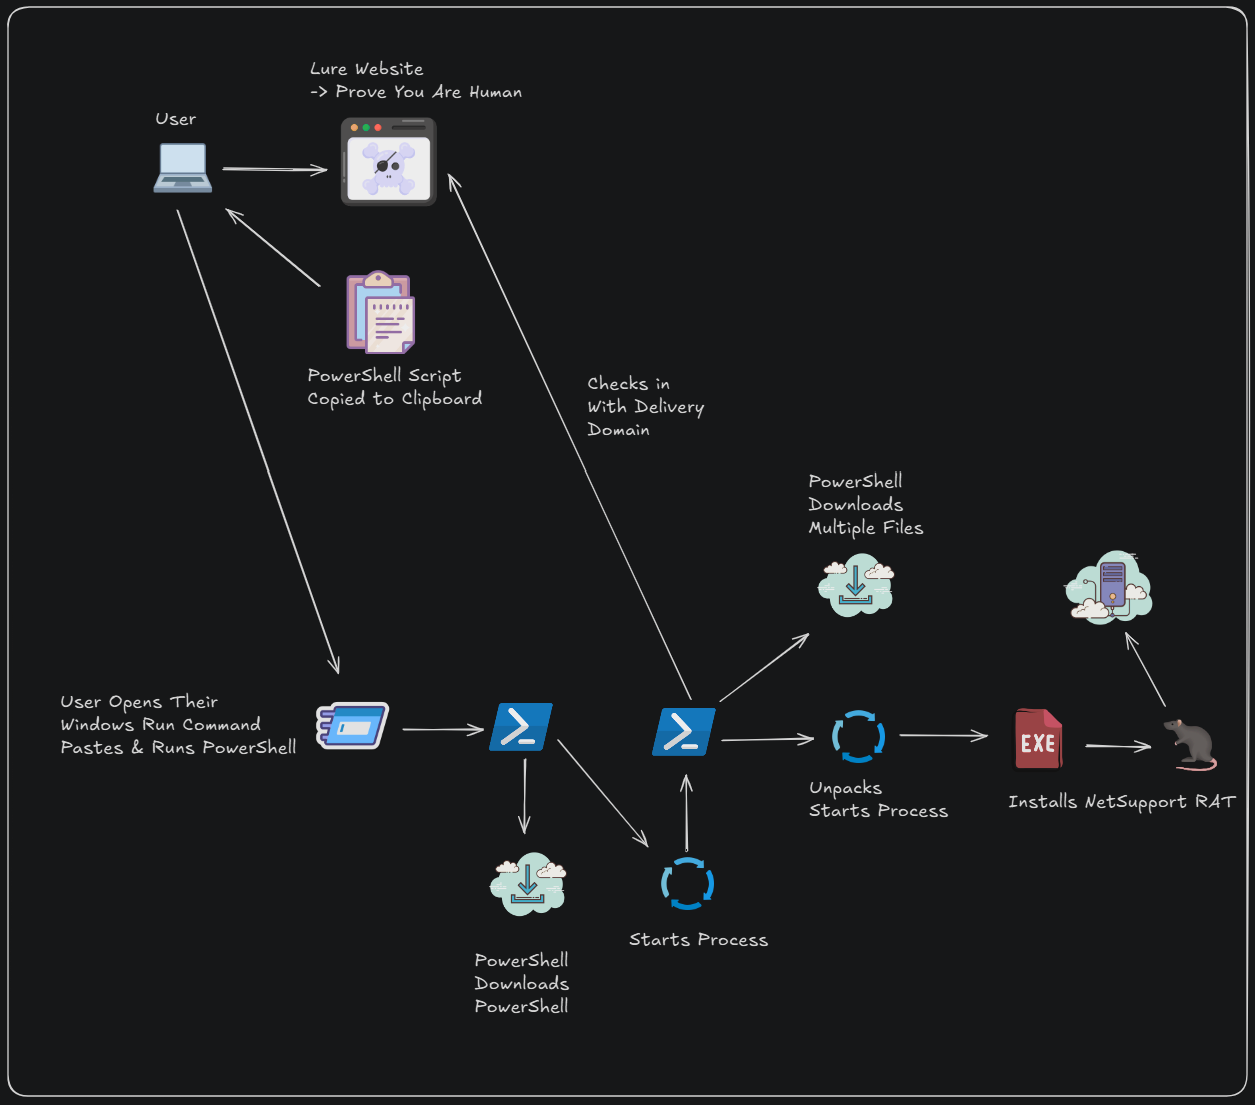
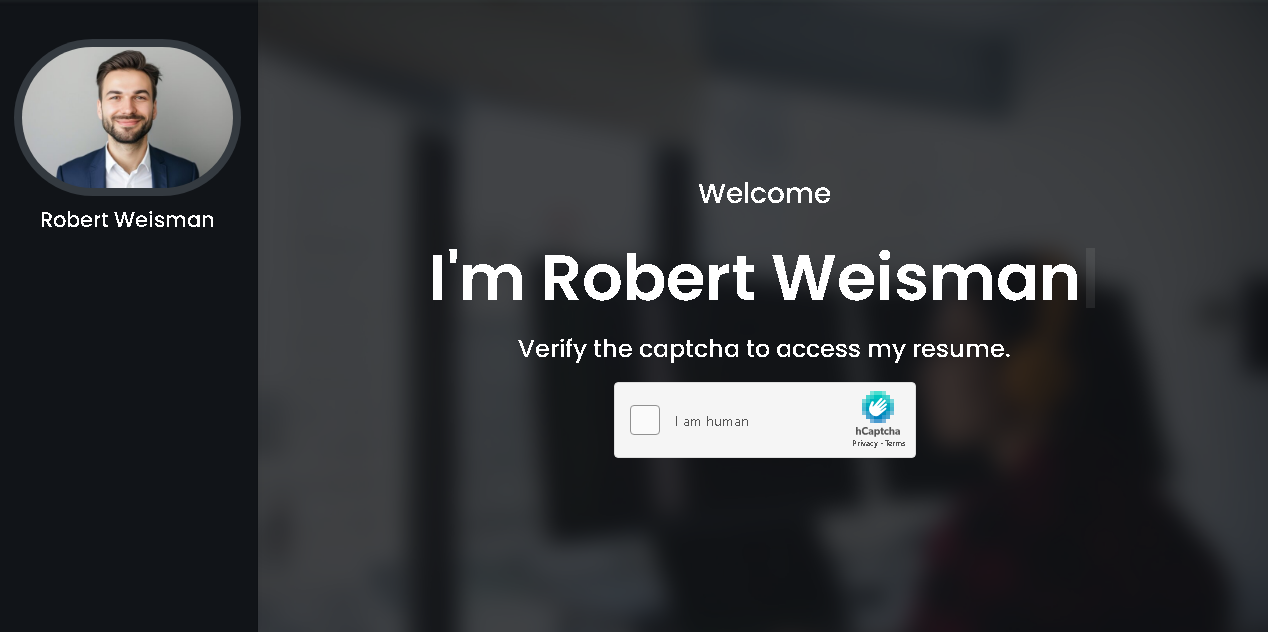
In our latest research, our team identified malicious multi-stage downloader Powershell scripts hosted on multiple themed websites including Gitcodes and fake Docusign captcha verifications. These sites attempt to deceive users into copying and running an initial powershell script on their Windows Run command. Upon doing so, the powershell script downloads another downloader script and executes on the system, which in turn retrieves additional payloads and executes them eventually installing NetSupport RAT on the infected machines.
🕸️ Skeleton Spider (FIN6): Trusted Cloud Malware Delivery
This research combines technical insights and practical analysis for both general audiences and cybersecurity professionals. We examined how FIN6 uses trusted cloud services, such as AWS, to host malicious infrastructure, evade detection, and ultimately deploy malware through socially engineered lures.
🛰️ Mapping Hidden Alliances: Russian-Affiliated Ransomware Ecosystems
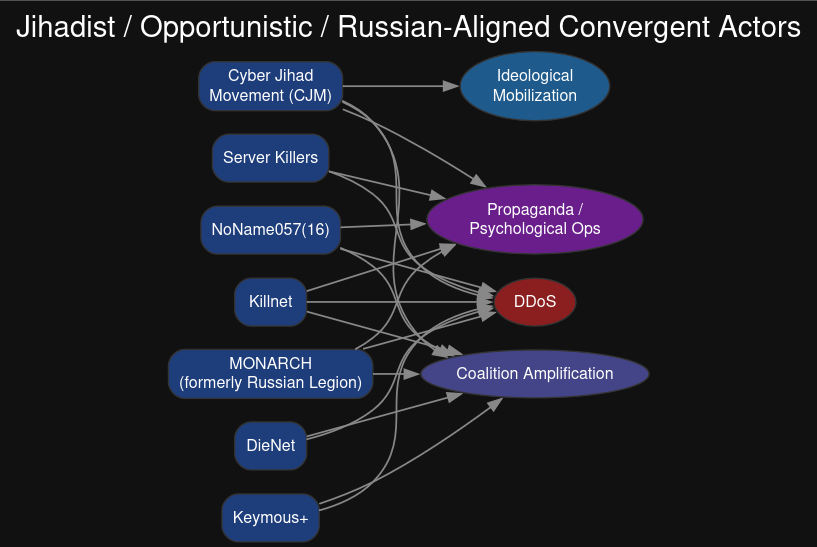
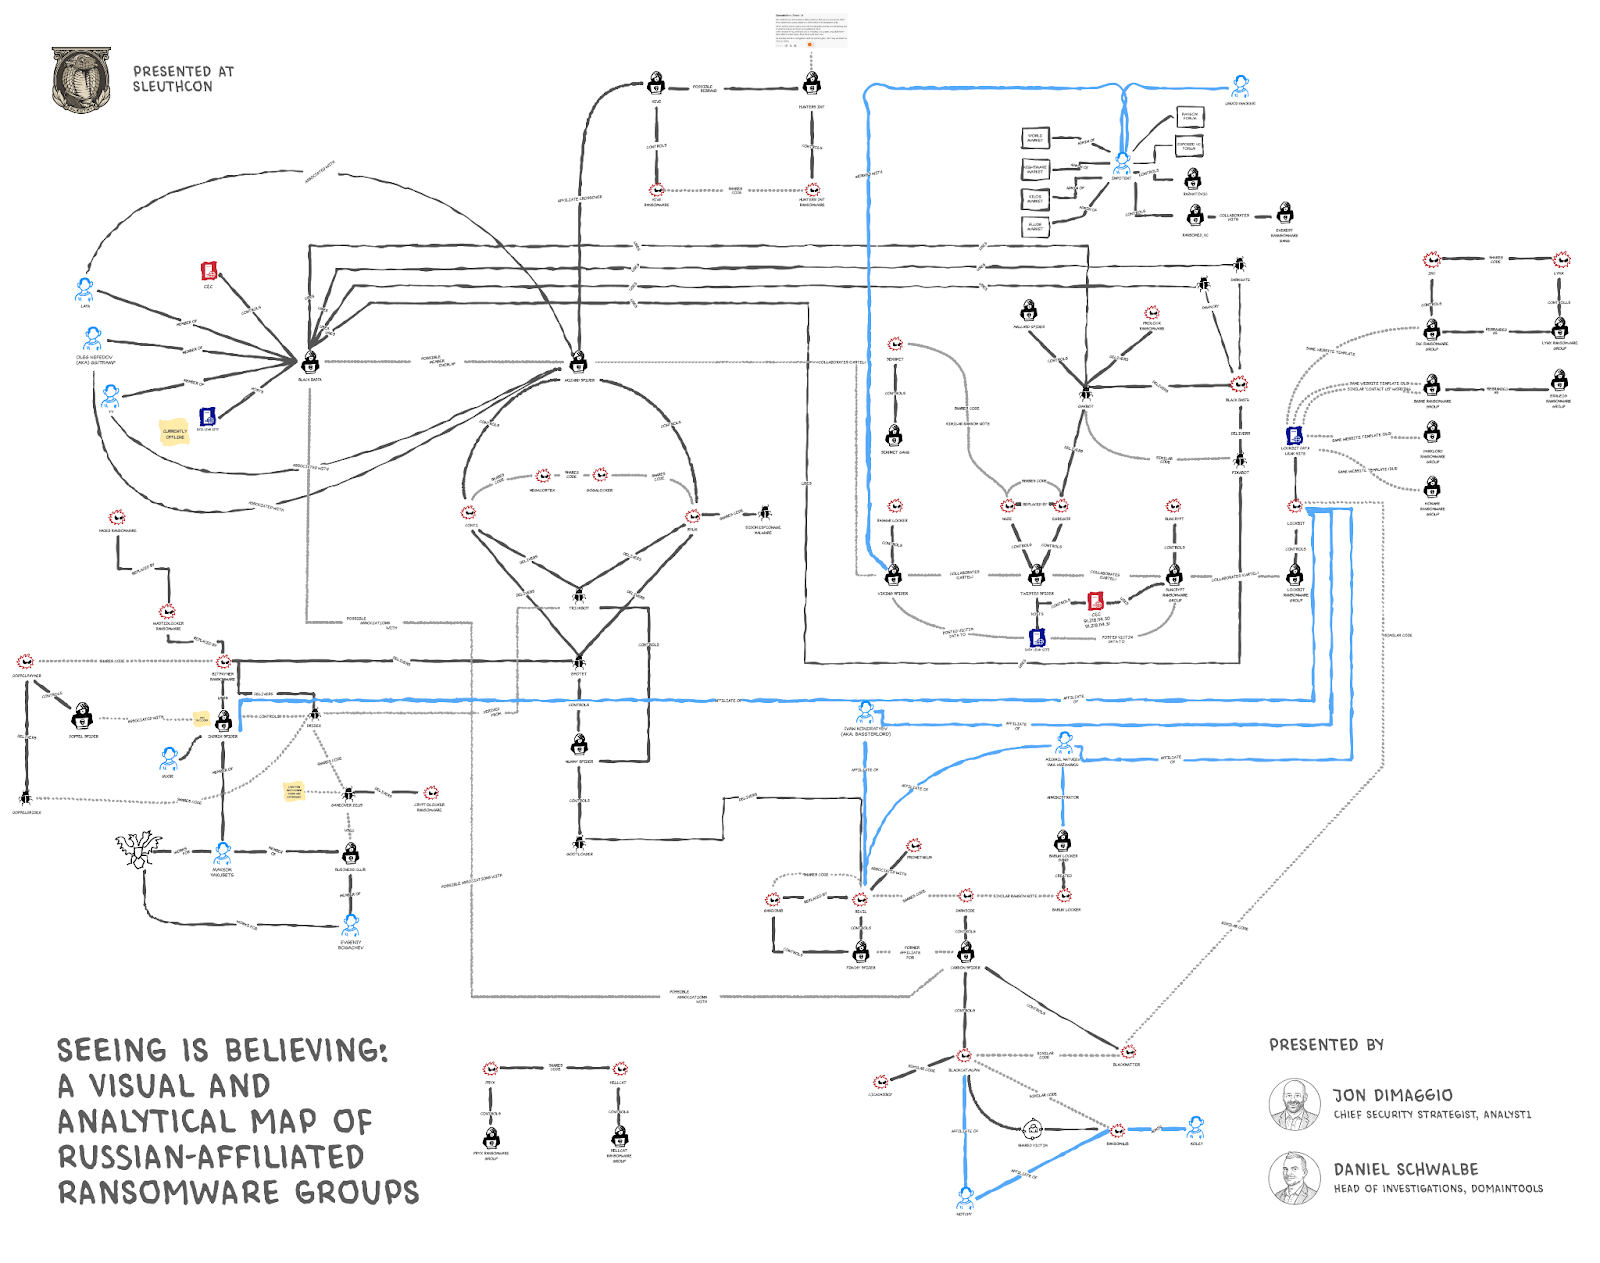
Jon DiMaggio at Analyst1, Scylla Intel, and our team dove into Russian-affiliated Ransomware Groups. This work follows previous research DomainTools undertook in tracking ransomware families and provides a visual representation of hidden connections between criminal factions, going beyond just mapping “families” to understand the intricate relationships between them. The core focus was on identifying overlaps in human operators, code fragments, infrastructure, and TTPs.
Jon and I presented this at SLEUTHCON - to see our presentation, 👍& 🔔to the SLEUTHCON YouTube page.
Cybersecurity Schlolastic Book Fair
Ian Campbell’s June Recommended Reading digest:
- Qualys – Inside LockBit: Defense Lessons from the Leaked LockBit Negotiations
- Proofpoint – The Bitter End: Unraveling Eight Years of Espionage Antics—Part One
- Mandiant – Hello, Operator? A Technical Analysis of Vishing Threats
Where We’ll Be
- FIRSTCon25, June 23-27
- Are you here this week? Come find our team as we sponsor this wonderful event!
- Hacker Summer Camp, August 3-10
- Come say hi to our team at The Diana Initiative, BSidesLV, Black Hat, or DEF CON! We will also have
Final Thoughts
Again, if you’re a returning reader from last month, I thank you. If you’re new, I hope you found this newsletter informational, helpful, and worthy of sharing with your peers.
We share this newsletter via email as well - if you’d prefer to get it to your inbox, sign up here.
If you missed last month's content, here are some quick links:
- Inside a VenomRAT Malware Campaign
- Hidden Threats of Dual-Function Malware Found in Chrome Extensions
- Scams and Malicious Domains Emerging from Breaking News
Thanks for reading - see you next month!
Daniel